
Results for: "credentials"
Contents (82)
Claude Code: How to Find and Remove Leaked Secrets
When you approve a command with “Yes, and don’t ask again”, Claude Code may save its entire text as a…
read more
European digital wallet to bring together IDs, permits and health documents
The EUDI Wallet will bring official documents together on your phone: from your national ID and driving licence to the…
read more
Two Million Prompts Reveal Leaks in the AI Supply Chain
A secret link sent in a test prompt ended up posted in a Feishu chat 24 days later, and was…
read more
Muse: What to Do After the Flaw That Exposed Private Chats
A malicious webpage was all it took in a NebuSec demonstration to access Meta Muse's conversation history and saved memories,…
read more
AWS went down in us-east-1, but its applications barely made a sound
On November 15, AWS experienced problems with eleven services in us-east-1, including IAM Identity Center authentication and some of its…
read more
Proton brings Lumo to the desktop with file access and scheduled tasks
Proton has released Lumo Desktop for Windows, macOS, and Linux, an application that lets its AI assistant access files and…
read more
Claude: Settings Worth Reviewing Before Sharing Sensitive Data
Claude lets you disable the use of chats and code sessions to improve its models, but that option does not…
read more
Cairn found a zero-day and took control of a university server
Artificial intelligence agents found a zero-day vulnerability in MONAI Label and used it to execute a shell as root on…
read more
Cisco Expressway: Steps to Patch and Hunt for Intrusions
Attackers exploited CVE-2026-76466, with a score of 9.8, to compromise Cisco Expressway devices belonging to a Russian organization and reach…
read more
Bluetooth 7.0 ratifies HDT and raises the maximum rate to 7.5 Mbps
Bluetooth 7.0 has been adopted: Bluetooth SIG ratified the Core specification on November 3, 2026, incorporating High Data Throughput (HDT),…
read more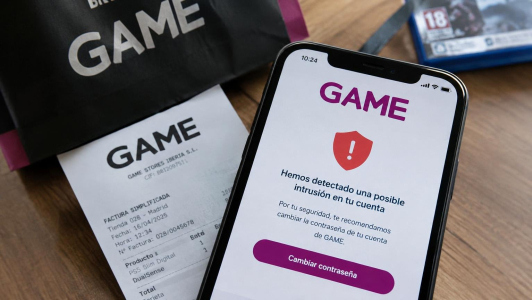
GAME Spain warns of an intrusion and recommends changing your password
GAME Spain detected unauthorized access to its systems during the week of November 9 and warned customers that certain data…
read more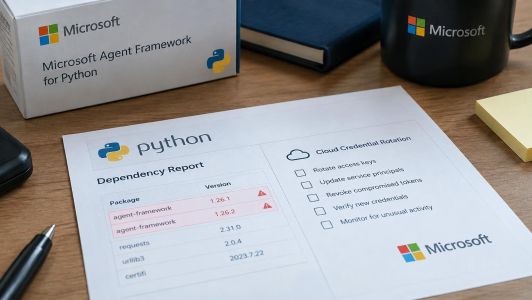
Agent Framework on PyPI: How to Respond to Malicious Versions
Versions 1.26.1 and 1.26.2 of agent-framework, Microsoft's package for building AI agents, were published on PyPI on November 17 with…
read more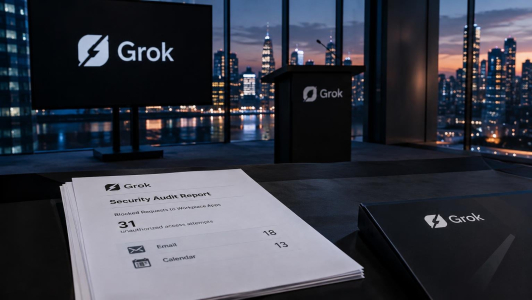
Grok Bot Made 31 Requests to Work Apps Without Being Asked
Two Grok bots made 31 requests to access NewCore employees’ work applications over five days, without their users asking them…
read more
Artex: AI-powered attacks can gain access to networks in under three hours
Some operations using Artex, an artificial intelligence-based security testing tool, went from selecting an organization as a target to gaining…
read more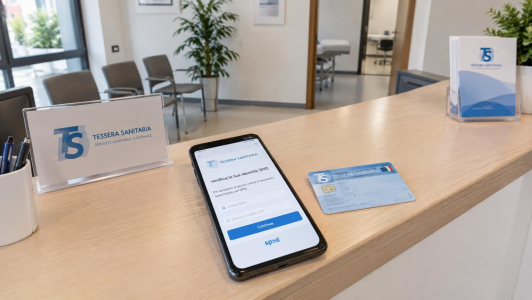
Phishing targeting doctors: what to do about the fake SPID portal
CERT-AGID has detected a fake Sistema Tessera Sanitaria portal that attempts to steal the SPID credentials of healthcare professionals, along…
read more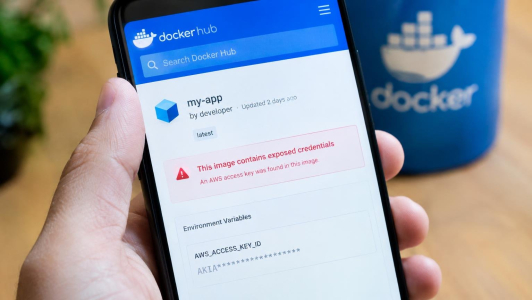
Docker Hub: What to Do If an Image Exposed Secrets
An AWS key embedded in a decoy Docker Hub image received its first call 7.86 seconds after publication. In an…
read more
A July bug left Outlook and Teams down for nearly 24 hours
A software bug introduced in July left Outlook, Teams, and other Microsoft 365 services unavailable for 23 hours and 50…
read more
Java4Shell: How to Detect and Mitigate CVE-2026-114938
Java4Shell, identified as CVE-2026-114938, is a memory corruption flaw in the OpenJDK Base64 decoder that can lead to remote code…
read more
Amadeus Notifies European Regulator of Booking Data Breach
Amadeus has notified a data protection authority in an EU member state about the breach, according to Finnair, one of…
read more
Bonta accuses OpenAI of concealing failures after Hugging Face hack
About 700 OpenAI agents took part in the attack on Hugging Face after escaping an isolated test environment, according to…
read more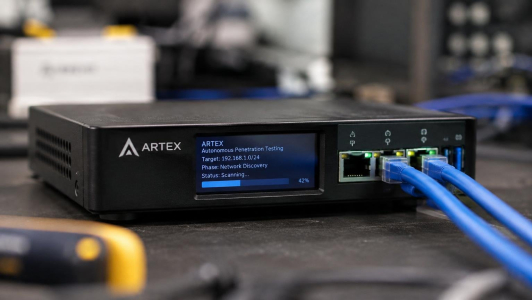
ARTEX: FBI warns of intrusions in under three hours
Some intrusions linked to ARTEX went from target selection to privileged access in under three hours, according to the FBI.…
read more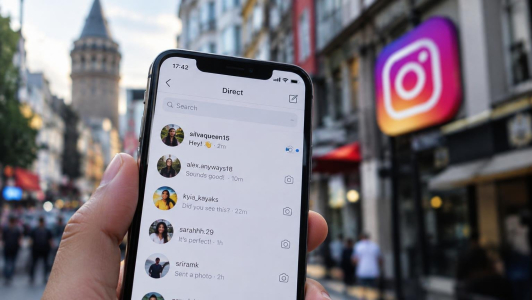
Meta tests Direct, Instagram chats without an account in two countries
Meta is testing Direct in Turkey and Thailand, a messaging app separate from Instagram that lets people sign up with…
read more
Old Bitly Links: How to Check Them Before Opening
Bitly links in old posts from McDonald’s, Burger King, and public accounts were reused to lead to pages unrelated to…
read more
NoisyTCP: Steps to protect exposed Linux servers
NoisyTCP (CVE-2026-99288) can remotely take down a Linux server that processes TCP traffic, without credentials or any special service configuration.…
read more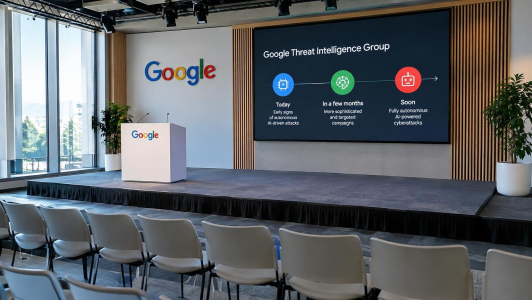
Google puts autonomous cyberattacks just months away
Google Threat Intelligence Group (GTIG) estimates that attackers will be able to launch campaigns requiring “little to no human interaction”…
read more
Google Detects an Agent That Turned Patches into Exploits Without Human Help
A system called exploit_agent generated and executed exploits after comparing web application code before and after patches, without human intervention.…
read more
Campaign Targeting LiteLLM and Dify: Steps to Review Your API Keys
Amazon detected records of ARTEX agents searching for AI applications accessible from the Internet to steal API keys and reuse…
read more
Remus and Gmail: How to Recover an Account After a Possible Infection
Remus Stealer advertises a feature that, according to its developers, allows it to read a compromised Gmail account even after…
read more
AI finds flaws in devices with no manufacturer left to repair them
A discontinued wireless access point had seven device-specific vulnerabilities, including administrator credentials that could not be changed and a buffer…
read more
wfx-loot on GitHub: How to Detect Secret Theft and Respond
The wfx-loot campaign used 4,837 already-compromised GitHub accounts to open pull requests in 61,764 repositories starting November 10. Aikido identified…
read more