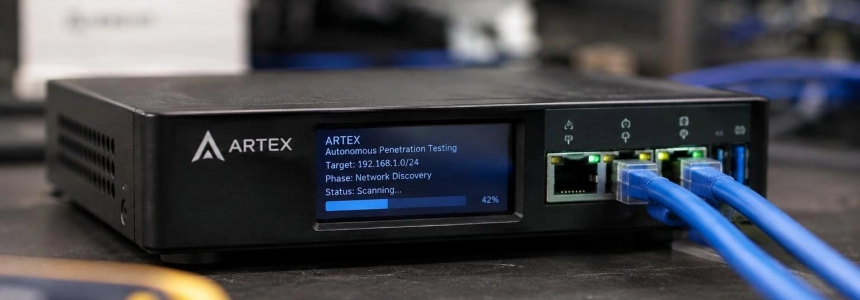
Some intrusions linked to ARTEX went from target selection to privileged access in under three hours, according to the FBI. The alert, published on November 13, links the attack framework to campaigns against at least ten sectors, including finance, defense, healthcare, and legal services.
The FBI warns that the tool enables complex operations against many targets at once, even with little experience. ARTEX does not include its own model: it can connect to models from Anthropic and OpenAI, as well as others of Chinese origin. On the attackers' servers, DeepSeek's Flash models were the most widely used, according to the FBI, which describes them as inexpensive and lacking visible safeguards when requests are presented as penetration tests.
The framework also appears in two major incidents: the theft of personal data belonging to customers of South Korean financial institutions and the compromise of ConnectWise's supply chain, which affected more than 2,250 downstream customers. However, figures for the number of people affected in South Korea differ across reports: TNW attributes a figure of about 67,000 to the FBI, while TechCrunch reports at least 68,000.
An open framework that continues to circulate
A person using the name “Autumn-27” published ARTEX on GitHub in July. In its first ten weeks, it garnered between 1,500 and 2,000 stars, according to TNW. The developer presented it as a tool for authorized testing; after reports of its abuse emerged, they removed the repository on October 8.
Removing it did not eliminate the copies. The FBI says forks, mirrors, and archived files are still circulating, along with a paid version called ARTEX PRO. Researchers counted more than 1,600 ARTEX consoles exposed to the internet in early November; the FBI considers it likely that the actual number of installations is much higher.
Microsoft describes ARTEX as a system of multiple agents based on language models, written in Go and with a Next.js interface. Its agents can carry out a penetration test from reconnaissance through data exfiltration with little human intervention, and record assets and vulnerabilities in a shared graph. The interface and results use English by default, although the system can also be configured in Korean, Mandarin, Spanish, or Japanese.
ConnectWise: access to applications and the cloud
Microsoft places Storm-0940's use of ARTEX, by a China-aligned actor active since 2021, as early as September 2026. The company attributes the ConnectWise compromise to this group and describes automated attacks against hundreds of organizations across various sectors. Its assessment says the tool accelerated reconnaissance, password spraying, and OAuth application abuse at downstream customers of the platform.
The sequence first involved a campaign targeting Microsoft 365 and Exchange Online accounts. Between October 10 and 14, Storm-0940 infrastructure launched password-spraying attacks against 327 accounts at eight organizations. Microsoft recorded more than 151,000 failed attempts: on October 11, the rate reached 2,900 per minute, and more than 111,000 failures occurred in a single day. It observed no successful authentications, token issuance, Graph calls, or directory changes during that campaign.
On October 15, public reports began to emerge about the compromise of ConnectWise's cloud backup application. A ConnectWise alert published the following day included indicators that matched infrastructure Microsoft had previously observed. After taking control of identities for several ConnectWise cloud applications, the agents attempted to sign in to more than 2,250 customer environments, taking advantage of the access those applications already had.
In several environments, Microsoft observed post-authentication activity through Microsoft Graph: reconnaissance, changes to application credentials, and privilege modifications that could expand or maintain access. The company clarifies that detecting an affected application or a successful authentication does not, by itself, prove that data was accessed or extracted. It also states that the activity described was not caused by a vulnerability in or compromise of Microsoft's corporate systems, products, or services.
| Activity described by Microsoft | Period or scope | Observed outcome |
|---|---|---|
| Password-spraying campaign | October 10–14; 327 accounts at eight organizations | More than 151,000 failed sign-ins; none observed to be successful |
| ConnectWise compromise and subsequent activity | From October 15; more than 2,250 downstream customers | In some environments, privileged access and Microsoft Graph operations |
| Automated intrusions linked to ARTEX | Hundreds of organizations across several sectors | In several cases, privileged access in under three hours |
Amazon detects key theft and deepfake testing
Amazon observed another facet of the campaigns. Between October 3 and November 5, its MadPot honeypot sensors received requests from ARTEX agents targeting services that simulated language model inference interfaces. The requests included operation logs from the agents themselves. Amazon assessed with moderate confidence that ARTEX had been used in these campaigns, based on references to the tool and other technical traces.
The most prominent operation sought API keys and other credentials to access AI models. The agents reused stolen keys to pay for the inference that powered new credential searches, turning the theft into an operation that funded its own expansion. Targets included gateways such as LiteLLM and application builders such as Dify and Ollama.
The logs also described searches across GitHub repositories and event files, npm and PyPI packages, container image layers, notebooks, model hosting sites, and Telegram channels. The agents validated credentials, checked their permissions, and sought access to premium models, secrets stores, and cloud AI services. Amazon says its sensors made it possible to observe this activity without exposing customer workloads.
A second campaign targeted identity checks at two cryptocurrency platforms. The agents tested real-time deepfake videos to bypass selfie checks and forged identity document photos. In the best recorded test, the face came within seven pixels of the requested position while completing the sequence of movements; even so, the provider's server rejected the deepfake in every recorded attempt.
In parallel, one session built a deepfake video pipeline on a consumer GPU using an open facial animation model. By splitting the model and avoiding unnecessary memory copies on the GPU, it reached 11.5 frames per second. The agents also described how they generated camera metadata and preserved JPEG compression tables so that altered images would look like original photographs at the file level.
“The agents succeeded where basic security practices were lacking, such as default or hardcoded credentials, keys exposed in code and public assets, unauthenticated interfaces and inference endpoints, and unpatched software.”
— CJ Moses, Chief Information Security Officer at Amazon
Barracuda rotated its customers' credentials
Barracuda reported another breach related to ARTEX. The tool found an exposed credential for an external service that the company had not revoked when its work with that provider ended. That access opened the way to credential stores that Barracuda uses to collect data from its customers' systems.
Barracuda's logs did not allow it to rule out the possibility that the attackers had accessed those credentials. The company chose to change all its customers' credentials. Its chief security officer, Arve Kjoelen, warned that those who wait to detect malicious activity before responding may arrive after the attacker has already finished. Barracuda told TechCrunch that it directly notified a minority of its XDR customers to revoke and recreate integration credentials, without specifying how many.
Separately, CrowdStrike linked ARTEX to a campaign against South Korean financial institutions that was active from late September to early October. The company found Claude Code session histories, ARTEX configuration files, and Claude memories in open directories. Based on this data, it described a two-server architecture and the use of DeepSeek v4.1-flash as the primary model, along with GLM-5.3 and Grok 4.6 in additional sessions. CrowdStrike did not attribute the campaign to a known actor and assessed it as likely, with moderate confidence, to be Chinese-speaking and financially motivated.
Assessments of the origins are not identical: Microsoft links the ConnectWise case to Storm-0940, while Amazon attributes its campaigns with moderate confidence to separate China-based groups. Google also included ARTEX among several AI attack frameworks in its latest threat report, published on Monday, according to TNW.
What the FBI and Microsoft recommend reviewing
The FBI asked organizations to inventory all their internet-accessible systems, including partner portals and employee applications, and to keep administrative interfaces off the public internet. Microsoft advises reviewing sign-ins for service identities and looking for unexpected changes to application credentials, privileges, and Microsoft Graph activity.
For ConnectWise customers, Microsoft recommends keeping affected connections disabled until formal restoration instructions are received, preserving relevant logs and evidence, and reviewing environments where affected applications are installed or have been authorized. It also warns against deleting enterprise applications as a first step: their configuration and available evidence should be preserved first. The review should cover activity from at least October 15, 2026.
Amazon advises treating AI applications, model gateways, and inference endpoints as production systems, and monitoring for unexpected spending or anomalous usage. The developer removed the original repository, but ARTEX copies remain available as the FBI warns that the tool continues to be used against organizations.
Sources: TNW | Security, Microsoft Security Blog, Amazon Web Services, CrowdStrike, TechCrunch