
Results for: "attack"
Contents (183)
NoisyTCP: Steps to protect exposed Linux servers
NoisyTCP (CVE-2026-99288) can remotely take down a Linux server that processes TCP traffic, without credentials or any special service configuration.…
read more
Google puts autonomous cyberattacks just months away
Google Threat Intelligence Group (GTIG) estimates that attackers will be able to launch campaigns requiring “little to no human interaction”…
read more
The bug that left 80% of Microsoft 365 gateways unresponsive
More than 80% of the affected network servers stopped responding during the global Microsoft 365 outage on November 12 and…
read more
Google Detects an Agent That Turned Patches into Exploits Without Human Help
A system called exploit_agent generated and executed exploits after comparing web application code before and after patches, without human intervention.…
read more
Campaign Targeting LiteLLM and Dify: Steps to Review Your API Keys
Amazon detected records of ARTEX agents searching for AI applications accessible from the Internet to steal API keys and reuse…
read more
FAA investigates network failure after grounding flights across the U.S.
A surge of data destabilized legacy equipment on the U.S. Federal Aviation Administration (FAA) communications network and forced the suspension…
read more
AI finds flaws in devices with no manufacturer left to repair them
A discontinued wireless access point had seven device-specific vulnerabilities, including administrator credentials that could not be changed and a buffer…
read more
Microsoft 365 outage reignites the battle for European digital sovereignty
For nearly 24 hours, the outage of Outlook and Teams in 74 countries left millions of users without their usual…
read more
uBlock Origin: How to Protect Yourself from the Selector XSS Flaw
A malicious page could add trusted filters to uBlock Origin and use that capability to execute JavaScript on other sites.…
read more
FaceStealer: What to Do About a Fake Zoom Video Call
On November 12, 2026, the FBI warned about FaceStealer, a scam that impersonates known contacts in fake video calls and…
read more
wfx-loot on GitHub: How to Detect Secret Theft and Respond
The wfx-loot campaign used 4,837 already-compromised GitHub accounts to open pull requests in 61,764 repositories starting November 10. Aikido identified…
read more
SignDrop on Windows: How to Check If Your Device Is Exposed
SignDrop is a public exploit that can allow a local user to escalate their privileges to SYSTEM on Windows by…
read more
Phantom Blade Zero: 50 Hours of Kung Fu Between Hits and Missteps
Some 50 hours of combat are enough for Phantom Blade Zero to show its two sides: a fighting system that…
read more
A saturated router after copper-to-fiber replacement grounded flights across the U.S.
A router overloaded the U.S. air traffic control network after L3Harris replaced copper wiring with fiber optics at a remote…
read more
Chrome: Update now to fix flaw CVE-2026-125350
Google has released an emergency update for Chrome desktop that fixes CVE-2026-125350, a flaw in the XML component that was…
read more
AI Agents: Five Gaps That Emerge When They’re Connected to the Enterprise
An agent built in ten minutes to read emails, match invoices against the ERP, and summarize them in Slack ends…
read more
OpenAI introduces Daybreak to test applications and prepare patches
OpenAI introduced Daybreak on November 12: a platform with two AI agent tools for testing web applications and helping prepare…
read more
SignDrop on Windows: Check CLFS Mode and Don’t Disable It
The public SignDrop exploit targets CLFS, the Windows logging system, and can elevate a local user’s privileges to SYSTEM, according…
read more
Uber Confirms Theft of Thousands of Driver’s Licenses
Hackers stole driver’s license data from thousands of Uber drivers in the United States after breaching Fireworks AI, a technology…
read more
Attacks on Check Point Wipe VMware ESXi Servers: Response Guide
A campaign targeting Check Point gateways began on October 30, 2026: attackers broke in through vulnerable Mobile Access portals, escalated…
read more
PostgreSQL: 52 vulnerabilities—how to check and update your servers
On November 12, PostgreSQL released updates fixing 52 vulnerabilities, including CVE-2026-6460: a type confusion flaw that could allow a user…
read more
Anthropic’s IPO Receives Six Times More Orders Than Shares
Orders to buy Anthropic shares in its IPO amount to six times the available supply, according to Bloomberg, as cited…
read more
GitHub and wfx-loot: Steps to Detect and Contain Secret Theft
The wfx-loot campaign affected 4,837 compromised accounts and tested write permissions across 61,764 GitHub repositories; in at least 1,835 of…
read more
SilentAir intercepts calls and 2FA codes from Asian mobile networks
SilentAir has intercepted two-factor authentication codes after diverting its targets’ messages through compromised equipment inside Asian mobile carriers. Enea, a…
read more
Microsoft rules out a cyberattack after more than 18 hours of outage
Microsoft attributes the Microsoft 365 outage to its own servers, not to a cyberattack: several Exchange Online machines became unavailable,…
read more
CVE-2026-119618 in Apache: How to Check Whether Your Server Is Exposed
Apache fixed a critical remote code execution vulnerability in the mod_http2 module in version 2.4.71. It affects Apache HTTP Server…
read more
CVE-2026-119618 in Apache: How to check whether your server is exposed
Apache fixed a critical remote code execution vulnerability in the mod_http2 module in version 2.4.71. It affects Apache HTTP Server…
read more
Four NGOs call for a halt to new AI models from five giants
Four nonprofit organizations have taken Google, OpenAI, Anthropic, Meta and SpaceX to the San Francisco Superior Court, seeking to halt…
read more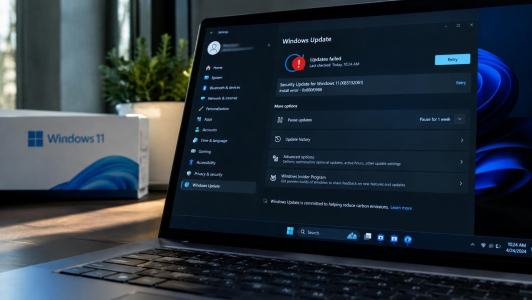
KB5132061 fails to install: Microsoft promises to fix it within 48 hours
The security update KB5132061 gets stuck during installation on some Windows 11 devices and returns errors such as 0x80070306, 0x800f0989,…
read more
Outlook leaks NTLMv2 hashes in exploited flaw: Microsoft fixes it
A maliciously crafted Outlook file could cause the application to connect to an attacker-controlled server and reveal authentication information. Microsoft…
read more