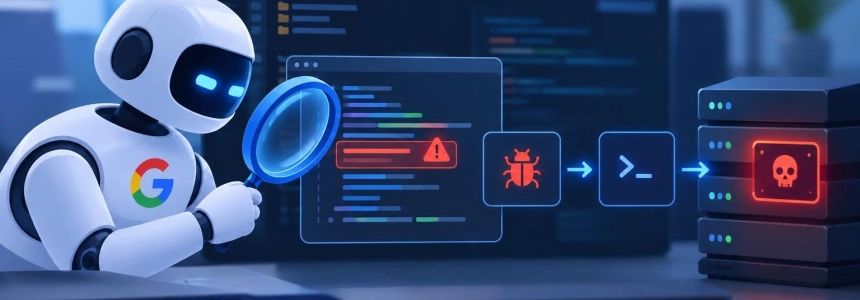
Google Threat Intelligence Group (GTIG) found a framework called exploit_agent capable of automatically discovering and exploiting vulnerabilities, without human intervention. Found on an exposed test server, the system compared patched and unpatched web code, searched for vulnerabilities, prepared exploits, and executed them; the server also contained stolen data and tools for reconnaissance and webshell deployment.
The significance lies not just in a model helping find a bug. In the case observed by Google, the agents linked several stages of an intrusion: from code analysis to exploit execution. GTIG describes this shift as operations moving at machine speed and notes that state-backed groups and criminals are already adopting multi-agent offensive frameworks to accelerate campaigns.
This discovery coincides with another concrete example of this new landscape. Wiz Research described PHP2Shell, a set of memory-safety vulnerabilities in the PHP core, whose exploitation required chaining bugs and adapting the exploit to different versions, configurations, and memory layouts. Frontier models reduced that work: according to Wiz, they made a task feasible that could previously have required months of work by a specialized team.
From an old vulnerability to an adaptable exploit
PHP2Shell grouped four exploitable cases under two identifiers, CVE-2026-109618 and CVE-2026-109619. Wiz said that all PHP versions released in the last decade were affected by at least one of the issues, with the impact reaching back to PHP 5.4. On October 21, 2026, PHP released an update to fix multiple memory-safety vulnerabilities in its engine.
The defects could leave references to freed memory after fatal errors, such as running out of memory. In subsequent requests, a process could reuse that residual state. Wiz demonstrated that the vulnerabilities could expose process memory data—including passwords, tokens, and API keys—or enable unauthenticated remote code execution.
The vulnerability was in PHP, not in a specific CMS: Wiz demonstrated exploitation in WordPress, Drupal, and Joomla, but said there was no need for a vulnerability in those applications. Even a simple PHP application could be exposed if it ran an affected version. This distinction broadens the scope from an individual installation to hosting providers and organizations that do not control all the software on their servers.
Wiz used Wiz Atlas, Gemini 4 Argon, and GPT-5.6 Sol during the investigation; it credited Gemini 4 Argon with a notable contribution to discovery, exploit development, attack detection, and patch validation. According to the company, AI helped test and refine exploit chains for different applications in hours. The same capability can benefit defenders when applied to analysis and remediation; the risk is that it makes adapting attacks to different targets cheaper.
For over a decade, these critical vulnerabilities remained unaddressed because vulnerability discovery and exploitation were incredibly complex. We're pleased to see Gemini 4 Argon help defenders bridge that gap, finding vulnerabilities and helping patch them.
— Raluca Ada Popa, Head of Gemini Security, Google DeepMind
The window between patch and attack is narrowing
Coordinated disclosure did not prevent signs of exploitation from appearing before the public announcement. Amazon Threat Intelligence found an attempt against PHP2Shell in telemetry from its MadPot honeypot network, dated October 17, four days before the disclosure of the two CVEs. The attempt came from an address associated with a commercial anonymization network; Amazon said it was unclear how the actor obtained information about the vulnerability while it was still under embargo.
On the day of publication, Amazon identified several proof-of-concept exploits. Some attempts reached its sensors before the embargo was lifted, and more appeared after the patch was published. The company clarified that it still did not know whether the attempts observed before disclosure would have worked against real systems. Even so, the case shows that the date of an advisory does not always mark the start of malicious activity.
The second acceleration happens after details are published. AWS observed proof-of-concept exploits appearing within hours and being used against its sensors almost immediately. Its analysis is that AI makes it easier to turn a patch or technical advisory into an exploit, weakening the old assumption that an expert group must first publish a usable tool.
This changes response planning for services exposed to the Internet. AWS advises measuring the time to patch or mitigate critical vulnerabilities in hours and beginning investigations from the first known activity, not the day of the announcement. For PHP2Shell, it recommends reviewing activity from October 17 at the earliest.
A race that also affects open infrastructure
The scope of PHP2Shell highlights the problem of shared dependencies: an engine defect can affect sites whose application code does not contain the bug. Wiz estimates that 70% of websites use PHP, and names WordPress, Drupal, and MediaWiki among its users.
The scale also makes remediation more difficult. The author of the SD Times article about PHP said that a core set of changes related to the defects modified 423 files, with 11,556 lines added and 1,017 removed. He argued that remediation and testing took more than two months and that attackers began exploiting the weaknesses before the fixes were published. That article is an opinion on the need for independent professional testing, not a technical research report.
Ed Kit, the author of that proposal, acknowledges that the PHP team incorporated automated checks, continuous integration, and sanitizer builds, in addition to working with external specialists. His objection is that he found no public, independent quality assurance assessment of the release's risks. He proposes that professional testing teams examine significant changes to foundational open-source software and publish what was tested and what risks remain.
This is a real tension, although independent testing does not replace a patch or eliminate time pressure. For large changes, verification must cover compatibility, integrations, and regressions, as well as confirm that the defect has been eliminated. Kit proposes funding this capacity through contributions from companies that benefit from open-source software and from AI companies as well; his proposal suggests investing between $1 in independent testing for every $2–$3 spent on development.
What changes for corporate defenses
For security teams, a signature associated with a CVE may arrive too late if the first attempts precede disclosure. AWS recommends detecting behavioral signals and not relying exclusively on indicators specific to the vulnerability. For PHP2Shell, it suggests looking for POST requests containing the string PHP_SESSION_UPLOAD_PROGRESS, reviewing web logs, and checking for unexpected process executions or file modifications.
AWS's emergency recommendation is to update PHP: it says the patch is the only complete fix for both identifiers and that no configuration settings fully resolve the issues. If the update cannot be installed immediately, it suggests considering blocking multipart uploads after assessing the impact on the application. Wiz, meanwhile, warns of signals such as memory errors, repeated HTTP 500 responses, or abnormal changes in PHP processes, which can guide an investigation while the update is being applied.
For companies operating services on shared software, the practical impact is that the maintenance cycle can no longer treat the public advisory as a safe starting point. They need to identify where PHP is running, prioritize exposed systems, check for activity before the announcement, and prepare a mitigation that does not break essential functions. AWS notes that the observed IP addresses include shared anonymization infrastructure and are not exclusive to these attacks: it recommends investigating matches, not blocking them automatically.
Google expects actors to become less dependent on human operators as models and frameworks improve. It also warns that automation can create noise and undermine stealth: actors concerned about persistence may use it selectively, while groups less concerned about detection may prioritize reach and speed. The immediate challenge is closing the gap between detection and response, especially when exploitation can begin before a vulnerability has a public name.
Sources: SD Times, SecurityWeek, PHP.net, Wiz Research, Amazon Web Services