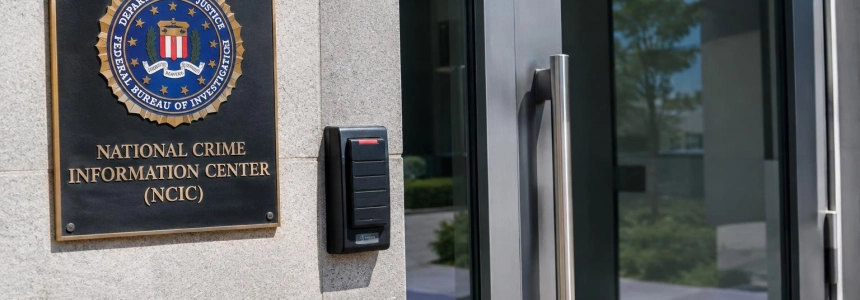
The FBI is investigating a possible intrusion into the National Crime Information Center (NCIC), the national database that allows U.S. law enforcement agencies to look up information about wanted people, arrest warrants, stolen vehicles, and other records. The breach, detected in recent days, would be the second known intrusion into FBI systems in two months; it is still unknown when it occurred or whether anyone obtained data.
The NCIC is operated by the FBI and serves to share law enforcement information among agencies at different levels of government. Officers use it during traffic stops, investigations, and background checks; its records include, among other data, missing people, weapons and stolen vehicles, protection orders, and outstanding arrest warrants.
What is known about the possible intrusion
The investigation was reported to CNN by two people familiar with the case, according to journalist Evan Perez. NBC News later confirmed that the FBI was investigating possible access to the system, also citing two people familiar with the inquiry. The FBI had not publicly commented on the incident by Friday night, according to both outlets.
The intrusion was reportedly discovered in recent days, but it is unclear when it began or how the attackers may have gained access. It is also unknown who was behind the access, whether information was extracted, or whether the system experienced availability issues. The FBI has not publicly identified any possible perpetrators, and BleepingComputer said it had also received no response to its questions.
The uncertainty is not limited to the possible exposure of sensitive data. A former FBI official who led investigations into cybercrime groups told CNN that the reliability of the records officers consult is also a concern.
“My concern isn’t simply whether hackers accessed sensitive information, although that is a problem, but whether they could compromise the accuracy of the information agents rely on.”
— Former FBI official quoted by CNN
Accuracy matters because the NCIC is used to verify identities, locate fugitives, and check outstanding warrants, according to the former official. CNN described the system as one of the country’s most important law enforcement information-sharing tools. There is no confirmation that records were altered or that the intrusion affected authorities’ queries.
A second intrusion in two months
The new case comes about two months after the extortion group ShinyHunters claimed to have breached systems associated with the FBI. In September, the group said it had stolen employees’ personal data from the agency through its job portal, FBIJobs.gov. BleepingComputer linked that attack to an unpatched vulnerability in Oracle PeopleSoft.
ShinyHunters claimed to have obtained information on around 38,000 FBI employees, according to the BBC, cited by TNW. The FBI opened an investigation. CNN reported that a Canadian researcher and author specializing in cybersecurity was arrested and faces charges related to that incident; BleepingComputer also described the person arrested as a Canadian cybersecurity executive allegedly linked to the attack.
After that breach, some FBI employees said they felt poorly informed about whether their data was among the stolen information and were disappointed with the security resources offered to potential victims, according to an earlier CNN report. That episode provides context for the new investigation, but there is no indication that the two attacks are connected. The NCIC intrusion has also not been attributed to ShinyHunters.
CNN’s coverage also recalled a separate incident in 2023 involving a computer system at the FBI’s New York office. That equipment was used in child sexual exploitation investigations and included a system for storing images related to the investigation of Jeffrey Epstein, according to CNN.
Kash Patel’s appearance
According to CNN, FBI officials already knew about the incident on Thursday, when agency director Kash Patel appeared on Fox News to discuss cybersecurity. Patel promoted Operation Winter Shield, an initiative urging companies to update their systems. CNN noted that the operation had ended months earlier, although Patel spoke about it as if it were still underway.
Patel said the administration was making updates to protect important systems and claimed previous administrations could have made them but did not. CNN and TNW reported his assessment that the FBI was getting ahead of problems and catching up. The interview therefore took place after agency officials had been informed of the possible intrusion, according to CNN’s account.
President Donald Trump also addressed the incident in a phone interview with Fox News on Saturday, according to CNN. He called it a negative development, but quickly linked it to his longstanding criticism of the FBI over its investigation into Russian interference in the 2016 election. Trump suggested the access could reveal information about that matter and other political episodes, without providing evidence, according to CNN.
Trump gave no specific details about the intrusion. CNN reported that he also used the conversation to mention his 2019 call to Ukrainian President Volodymyr Zelenskyy and his claims of alleged election fraud. Those remarks concerned Trump’s political grievances; they do not explain who accessed the NCIC or what information they may have viewed.
USDA faces another incident
The FBI investigation became known the same week as a cyberattack against the U.S. Department of Agriculture (USDA). NBC News reported that employees were notified on Thursday that one of the department’s systems had been attacked. USDA officials told NBC that the affected system is used to pay farmers and that, as of Friday, there was no indication that other systems had been hit.
The incident had operational effects: the USDA took numerous applications offline for several days, according to Nextgov/FCW and Government Executive, cited by TNW. The disruptions affected several financial tools the agency uses to pay farmers. The department had not made public comments, according to the BBC, cited by TNW.
USDA officials warned that the attackers could find a path to more sensitive information. That possibility does not amount to confirmation that they succeeded. Neither agency has identified who may be responsible or what data may have been obtained.
Incidents and outages in other systems
News of both breaches came after several days of outages affecting private and public services. The Trump administration maintains that those problems are unrelated to one another and were not caused by cyberattacks.
The NSA’s classified computer network was down for several days after an outage on Tuesday. The problem occurred during maintenance work, and there were no signs of a cyberattack, sources told NBC News. By Friday, the network was back up and running. The available information does not establish a connection between that outage and the FBI investigation.
Senator Mark Warner, a Democrat from Virginia and the ranking Democrat on the Senate Intelligence Committee, said Wednesday that evidence indicated the technology outages were not due to cyberattacks. At the same time, he warned that artificial intelligence may have contributed to system vulnerabilities, according to NBC News. Separately, the White House confirmed that Sean Cairncross would leave his position as national cybersecurity director; TNW reported that Kirsten Davies, the Pentagon’s chief information officer, was replacing him.
For now, the central question remains unanswered: the FBI has not specified whether police records were accessed, whether they may have been altered, or whether NCIC queries were interrupted. The agency has also not said who may be behind the intrusion. Its investigation is ongoing.
باSources: BleepingComputer, TNW | Security, NBC News, KTVZ