OpenSSH 10.6p2 closes access with passwords up to 1,024 bytes long
A password string between 257 and 1,024 bytes was enough to log in over SSH to certain Linux accounts configured without a password. Disclosed on Nove...
An attacker who can modify traffic between APT and the package server can replace a verified download with their own package and execute its code as r...
948 local privilege-escalation exploits capable of gaining root: that is the result OpenAI attributes to a 30-hour run of its new automated pipeline o...
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) confirmed the exploitation of a WordPress core vulnerability and added it to its Know...
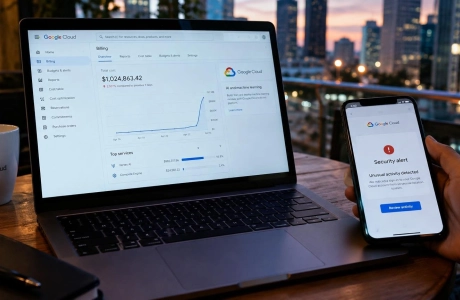
More than $100,000 in a single day and, in some cases, accumulated charges of up to one million: that is the cost Google and Mandiant attribute to att...
A fake job interview helped open the door to Binance’s wallet infrastructure: an employee downloaded a supposed coding exercise that installed malwa...
Playwright 1.64.1 includes Chromium without the patches for four vulnerabilities that Chrome has already fixed, a combination that could expose your c...
Synology has detected C3RB3R ransomware attacks against NAS devices running vulnerable versions of DiskStation Manager (DSM). The company says attacke...
A public ChatGPT conversation could become a way to execute JavaScript with the session of the person who opened the link. Parameter demonstrated that...
More than 1.3 million Android TV Boxes were incorporated into XCPE, a botnet that resold home internet connections and loaded malicious activity modul...