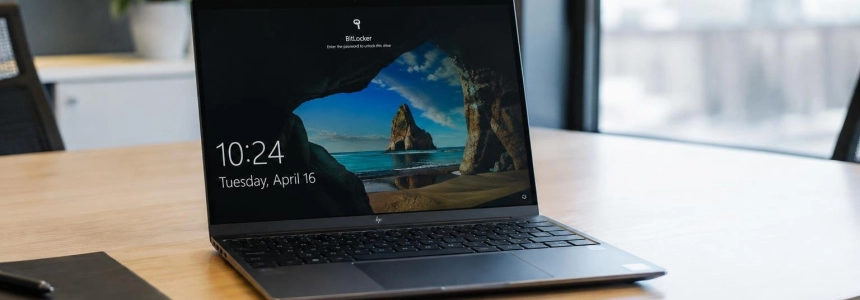
FastUnlock allows someone with physical access to a locked PC to run programs without signing in, according to ThreatLocker’s tests. The technique uses Narrator during Microsoft account recovery; the access the company obtained was to WSIAccount, which does not have administrator permissions. Microsoft has not yet published a fix, and no real-world attacks have been reported.
The technique does not decrypt BitLocker or recover its key: in a typical configuration, the TPM unlocks the drive during startup, and the data is already available when the lock screen appears. ThreatLocker reproduced the method; the researcher said they tested it on Windows 11 26H2 with the November updates. There is no official list of affected versions, so it is best to assess the risk based on usage conditions rather than assume a particular version is safe.
Check whether your device fits the scenario
The exposure described is local, not remote: the person must be able to handle the computer. In addition, a Microsoft account must be accessible through the recovery options on the lock screen. If someone can take a laptop, approach a shared device, or access an unattended computer, the screen lock alone does not cover that scenario.
The researcher reported Windows 11 26H2 as the test system and left Windows 10 untested. ThreatLocker confirmed its own reproduction of the limited access, but did not publish a list of affected editions or versions. The fact that the PC is up to date does not rule it out: the method has been presented as an unpatched zero-day.
Steps you can take now
Limit who can handle the device. Lock away laptops that are not in use, and control access to shared workstations or computers placed at counters. Physical access is the central condition for FastUnlock, so reducing opportunities for someone to handle the device directly addresses that condition.
Set a BitLocker startup PIN on sensitive devices. With this protection, the PIN is requested before Windows starts and the drive is unlocked. ThreatLocker notes that this helps if the device has just been powered on; this recommendation does not make encryption a defense against a device that is already at the lock screen.
Shut down or hibernate the device when it will be out of your control. Microsoft recommends this measure along with a startup PIN to defend against attackers with physical access. If the PC is already on and locked, the preboot PIN is not requested again; shutting it down or hibernating it before leaving it unattended therefore changes the state from which an attempt would have to begin.
Review which accounts are on the device. Check whether a Microsoft account can be used in the recovery flow from the sign-in screen. This condition is part of the published requirements for FastUnlock. It is not enough to know that there is a password: what matters here is whether recovery allows access to a Microsoft account.
Prepare a response for managed devices. If you manage an organization’s laptops, identify which ones could be physically accessible and which have a BitLocker startup PIN. Prioritize sensitive or easily removed devices, and apply measures using the tools and policies your organization already uses; there is no official Microsoft fix that can be installed now to close off FastUnlock.
Monitor Microsoft communications and apply an official update or recommendation if one is published. The Hacker News reports that Microsoft has not yet provided a solution; Cyber Kendra also notes that no advisory or patch had been published. Until then, the immediate response is to protect physical access and the startup process.
What BitLocker protects and what it does not
In the typical mode described by The Hacker News, the TPM allows the drive to be unlocked at startup without entering a PIN. When the lock screen appears, Windows has already started, and the system can read the files on the drive. FastUnlock works after that unlock: it does not break disk encryption, but instead seeks to run code from a locked session.
That is why a PC can have BitLocker enabled and still fit the scenario if it unlocks automatically at startup. A startup PIN adds a barrier before Windows and the drive become available. But it does not protect a device that has already started: shutting down or hibernating it before losing physical control also matters.
Mistakes to avoid
Do not treat the screen lock as sufficient physical protection. The disclosed method specifically targets a locked device that someone can handle.
Do not confuse limited access with full control. ThreatLocker obtained WSIAccount and specified that it is not an administrator account. The test does demonstrate a way to run programs without signing in, but it is not equivalent to automatically gaining administrative privileges.
Do not describe FastUnlock as a BitLocker decryption method. The technique takes advantage of the fact that the disk may already be unlocked when the sign-in screen appears. This distinction matters when deciding which measures to apply: a PIN before startup and physical control of the device.
Do not assume that every Windows version is affected. The published information does not establish a complete inventory: Windows 11 26H2 is listed as tested by the researcher, while Windows 10 is listed as untested. Microsoft has not provided an official list either.
Do not install supposed fixes or block components blindly. No official patch is available. Cyber Kendra mentions a proposal from the researcher to block Narrator using AppLocker or a DACL, but does not present it as a Microsoft solution. On managed devices, do not apply this change without having it validated by the responsible administrators.
The most concrete measure for a device that could end up in someone else’s hands is to combine a BitLocker startup PIN with shutting down or hibernating the device when it leaves its user’s control. Also keep an eye out for any official Microsoft advisory or update.
Sources: The Hacker News, Tom's Hardware, ThreatLocker, Business Upturn, Cyber Kendra