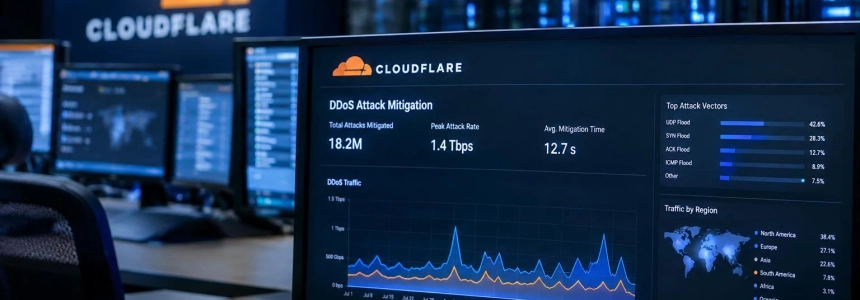
Cloudflare mitigated 18.2 million network DDoS attacks between July and September 2026: about 8,226 per hour, or one every 0.44 seconds. During the same period, the company blocked 14.4 trillion HTTP requests linked to DDoS attacks, according to its quarterly report prepared by Cloudforce One, its threat intelligence organization.
Network attacks increased compared with the previous two quarters: Cloudflare had recorded 13.2 million in the second quarter and 10 million in the first. However, the defining pattern of the period was not a succession of massive traffic floods, but the proliferation of short, repeated attacks.
Attacks lasting less than 10 minutes and staying below 1 Gbps increased by 208%, according to Cloudflare. The company links this profile to DDoS-for-hire services, known as booters or stressers. 96% of network attacks in the quarter ended within ten minutes, and 98% stayed below 1 Gbps.
“Short-burst, low-bandwidth attacks lasting under 10 minutes and 1 Gbps surged by 208%,”
— Cloudforce One threat intelligence team
Fewer massive attacks, more bursts
At the other end of the spectrum, attacks exceeding 1 Tbps fell from 805 in the second quarter to 251 in the third, a decline of nearly 69%. Cloudflare tentatively links the drop to law enforcement actions early in the year against four major botnets of connected devices: Aisuru, KimWolf, JackSkid, and Mossad.
The decline does not mean the threat has disappeared. Cloudflare points to the emergence of new variants, including Dysphoria and Evooo1Bot, and describes IoT botnets as a persistent threat to network infrastructure. Activity classified as Mirai also had an intense quarter: it reached 57.23 petabytes in August, accounting for 46.5% of the network bytes mitigated during the period. The longest sustained Mirai attack lasted 49.7 hours, from August 19 to 21.
Reflection attack activity also changed. CLDAP, which had grown sharply during the first half of the year, fell 99.5% from the previous quarter and accounted for just 0.05% of network attacks. By contrast, DNS amplification rose 215%, reaching 3.43% of the total. Generic UDP floods increased from 14.06% to 31.31%.
Targets span more sectors and countries
Media, production, and publishing remained the most attacked sector, although its share fell sharply compared with the previous quarter. Cloudflare also observed a shift toward other sectors: Internet ranked sixth, while consumer services and adult entertainment reached eighth and ninth place, respectively.
The United States ranked first among the countries targeted, ahead of China; Indonesia came third. Canada rose from 16th to sixth, with attacks targeting sectors such as retail, telecommunications, and marketing. Israel moved up seven places to tenth after recording sustained activity in mid-September.
Cloudflare says its systems detect and mitigate attacks autonomously. It also offers hosting providers, cloud computing platforms, and Internet operators a free DDoS Botnet Threat Feed to identify IP addresses and accounts associated with attacks. More than 800 networks have signed up, according to the company. New botnet variants and the growth of short bursts keep the report focused on a threat that is changing in scale and method.
Sources: The Hacker News, Cloudflare Blog, SiliconANGLE, eSecurity Planet